Direct Answer: Microsoft Agent 365 Cross-Cloud
Building an AI agent is getting easier. Knowing who owns it, which systems it can change, and how to shut it down is harder. Microsoft Agent 365 aims to provide a shared inventory, identity and oversight model for agents across supported platforms. The key distinction: central governance does not mean central execution. Agents still run in their own environments, where target systems must enforce access.
Architecture: Discovery, Registry, Identity, and Enforcement
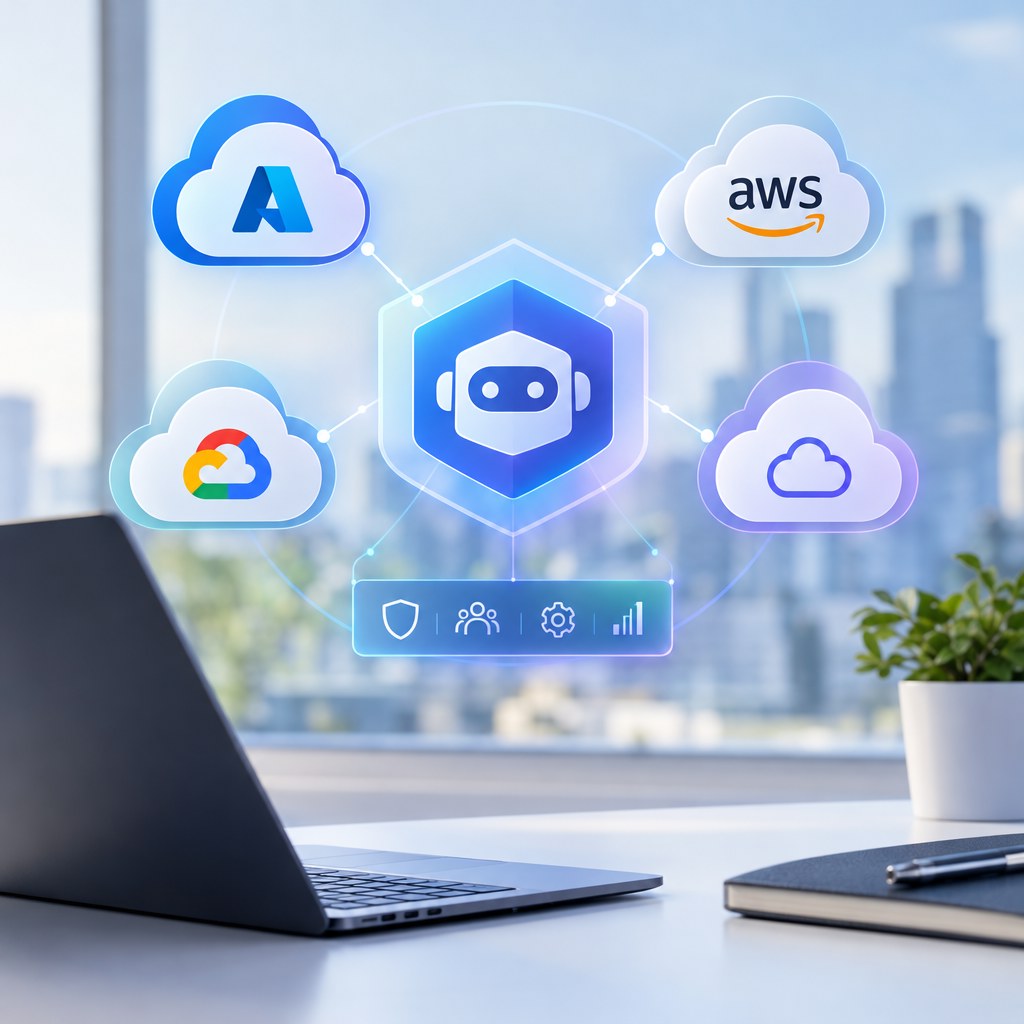
At a high level, Agent 365 sits between distributed agents and the enterprise systems they use. Connectors and discovery mechanisms surface metadata; a registry creates an inventory and ownership record; identity and security governance determine access. APIs, applications, and data services remain behind existing controls, while agent activity becomes more visible and governable.
Cross-cloud governance flow
This does not replace cloud-native controls. AWS, Google Cloud, Azure, SaaS platforms, and internal systems still need workload identities, network restrictions, logging, and permission models. The opportunity is coordination: a common administrative plane for risk, identity, and platform teams, while each environment enforces local controls.
Why Entra Agent ID Matters
An agent needs more than an API key in a workflow configuration. A durable enterprise approach requires a distinct identity, clear ownership, lifecycle management, scoped permissions, and auditable authentication events. Entra Agent ID treats agent identity as a first-class governance concern, separating human users, applications, and autonomous agents with different responsibilities and risk.
Where federation is supported, external runtimes may connect to enterprise identity policies rather than unmanaged credentials. Teams should verify token audiences, claims mapping, credential rotation, conditional-access behavior, and revocation paths. Unsupported or immature paths should stay isolated until their security model is validated.
What Cross-Cloud Governance Changes
Today, teams often track agents in separate cloud consoles, spreadsheets and service-account inventories. A common registry can improve ownership, reviews and incident response. But registration is not runtime enforcement: an agent can still make an unsafe tool call if the downstream API permits it. Keep authorization, approval gates and audit logs at the target system.
Benefits and Tradeoffs for Enterprise Teams
Benefit: consistent ownership, onboarding and incident response across supported agent platforms. Best fit: enterprises with multiple agent-building teams and a genuine auditability problem, rather than a single low-risk prototype.
Tradeoffs: onboarding friction, connector gaps and dependency on a shared governance ecosystem. Limitations: Agent 365 cannot by itself prevent prompt injection, faulty reasoning or unsafe downstream tools. Architects should verify the supported integrations and enforcement points before adopting it as a production control.
Production Readiness Checklist
Before production, validate one realistic workflow end to end. For example, use a customer-support agent that can read case history but cannot issue refunds without human approval.
Three-Step Production Validation
- Register and scope: assign an owner, record the agent and its environment in the supported inventory, and grant read-only access to approved case data. Evidence: owner, identity and permission mapping.
- Test the boundary: request a refund without approval. The refund API must reject the action even if the agent attempts it. Evidence: a denied API request and an auditable authorization decision.
- Revoke and trace: disable the agent or its credentials, verify subsequent calls fail, and correlate agent activity with downstream API logs. Evidence: a complete trace and documented rollback procedure.
Go/no-go: proceed only when access is least-privileged, unauthorized actions are blocked at the target system, and revocation and auditing work reliably.
- Assign named business, technical, data, and incident owners.
- Document intended tasks, prohibited actions, connected tools, and decision boundaries.
- Use least-privilege permissions and separate identities for development, testing, and production.
- Test tool calls for authorization failures, malformed inputs, prompt injection, and unsafe escalation.
- Define logging, retention, alerting, rollback, and emergency disable procedures before launch.
- Review external connectors for data residency, contractual, privacy, and support implications.
Preview Boundaries and Federation Questions
Microsoft’s Ignite 2026 updates describe continuing Agent 365 capabilities and direction, but enterprises should distinguish announcements from production-ready support in their tenant and region. Preview features can change, offer limited connectors, or impose operational constraints. Validate documentation, service terms, identity behavior, and support commitments before making any cross-cloud capability a mandatory control for regulated or critical workloads.
Conclusion: Govern Agents Before They Scale
Start with one read-only agent and one agent capable of changing business data. Assign owners, map tool permissions, test a denied action and emergency revocation, then trace the event across Agent 365 and the target API. If you cannot identify who authorized an action and where it was enforced, the design is not production-ready.