Where PHP deployments go wrong
For Azure solution architects, the central challenge in modern cloud engineering is not merely determining whether a specific security capability exists. Rather, it is verifying whether that capability can be deployed safely, operated reliably at scale, seamlessly integrated with an existing enterprise landing zone, and retired or rolled back without unexpected system downtime. When managing PHP workloads in cloud environments, relying on a single default Web Application Firewall (WAF) rule or basic perimeter defense is fundamentally insufficient. Modern security demands a rigorous, multi-layered approach that addresses identity management, network segmentation, robust secret handling, and continuous dependency hygiene. This article establishes a practical architectural decision framework and implementation blueprint for PHP Application Security on Azure, designed to help engineering teams build defense-in-depth controls tailored to real-world production constraints.

Why Cloud Architects Should Prioritize Comprehensive PHP Security
Building resilient, defense-in-depth controls for PHP applications hosted on Microsoft Azure requires looking far beyond standard perimeter filters. A sound cloud adoption strategy must carefully evaluate multiple interrelated vectors, including identity governance, explicit network boundaries, automated deployment pipelines, structured logging, data classification standards, disaster recovery protocols, and total cost of ownership. Preview features and emerging runtime capabilities require additional scrutiny regarding service limits, regional availability, and long-term support commitments.
Many legacy PHP applications carry technical debt that complicates cloud migration. Hardcoded database credentials, outdated framework versions, and unmanaged file upload directories can easily introduce severe vulnerabilities if they are not systematically addressed during the Azure architecture review phase. By establishing clear operational boundaries and leveraging modern Azure platform-as-a-service (PaaS) capabilities, organizations can significantly reduce their attack surface while maintaining developer velocity.
Harden the runtime and dependencies
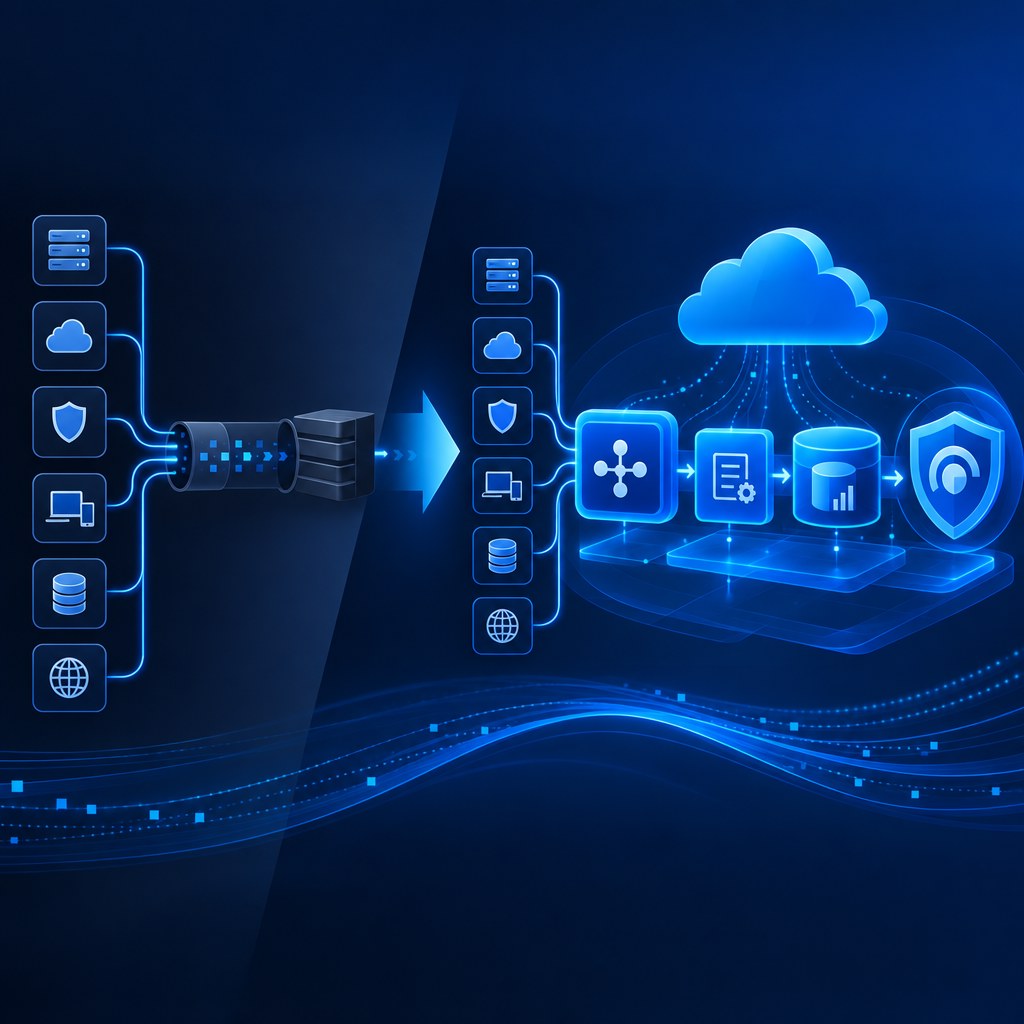
Implementing robust security controls for cloud-native PHP workloads follows a structured progression from foundational assessment to continuous monitoring. The conceptual delivery flow spans five distinct phases, ensuring that security is embedded at every stage of the application lifecycle rather than bolted on as an afterthought.
Discovery & Inventory
Catalog active PHP runtimes, third-party composer packages, and legacy dependencies across all subscriptions.
Identity & Secrets
Eliminate embedded connection strings by adopting Microsoft Entra managed identities and Azure Key Vault.
Network Isolation
Enforce private endpoints, restrict public ingress, and integrate Application Gateway with WAF policies.
Runtime Hardening
Disable dangerous PHP execution functions, enforce strict error handling, and secure session management.
Telemetry & Audit
Streamline diagnostic logs to Azure Monitor and configure real-time alerts for anomaly detection.
This sequence serves as a conceptual implementation model rather than an assertion that Azure exposes these exact steps as a single integrated product feature. Engineers must adapt this workflow to match their enterprise landing zone architecture, compliance requirements, and cloud governance frameworks.
Protect identity and secrets
Translating architectural principles into operational reality requires methodical design checkpoints. Each of the following operational checkpoints defines specific ownership boundaries, input and output expectations, failure modes, access controls, and verifiable evidence required prior to production rollout.
Inventory PHP Versions
Maintaining an accurate inventory of all active PHP runtimes across enterprise subscriptions is a critical design checkpoint. Unpatched or end-of-life PHP versions expose workloads to known Common Vulnerabilities and Exposures (CVEs). Organizations must define clear ownership for runtime lifecycle management, establish automated discovery mechanisms via Azure Resource Graph, and document fallback procedures in case a minor version upgrade introduces compatibility regressions.
Patch Framework and Dependencies
Vulnerabilities frequently enter PHP applications through third-party packages managed via Composer rather than the core PHP interpreter. Architectural governance must mandate automated dependency scanning within continuous integration and continuous deployment (CI/CD) pipelines. Teams need to define exact protocols for addressing high-severity advisory alerts, specifying expected turnaround times for emergency patches and regression testing protocols before deployment to staging environments.
Enable Managed Identity Where Possible
Eliminating stored credentials from application configuration files represents one of the most effective security improvements an architect can make. By leveraging Microsoft Entra managed identities for Azure App Service, PHP applications can authenticate securely to Azure Database for MySQL, Azure SQL, and Azure Storage without embedding connection strings in environment files or source code repositories. This operational checkpoint requires defining appropriate role-based access control (RBAC) assignments following the principle of least privilege.
Protect Secrets
For secrets that cannot be accessed via managed identity, such as third-party API keys, cryptographic salts, or external service tokens, Azure Key Vault serves as the secure storage repository. Applications should fetch secrets at runtime or leverage App Service configuration references tied to Key Vault. Operations teams must establish strict access policies, audit logging for secret retrieval, and automated key rotation schedules to minimize exposure risk.
Monitor App and WAF Telemetry
Visibility is vital for detecting and neutralizing security incidents. This operational checkpoint involves routing application diagnostic logs, web server access logs, and Azure Web Application Firewall (WAF) telemetry into a centralized Log Analytics workspace. Security operations teams must define alert rules for anomalous request patterns, high error rates, and blocked SQL injection or cross-site scripting attempts.
Prove the controls work
A resilient governance model relies on clear enforcement mechanisms integrated directly into cloud infrastructure. Use Microsoft Entra identities wherever supported by underlying Azure services, enforce least-privilege RBAC assignments, store application secrets exclusively in Azure Key Vault, establish explicit network trust boundaries using private endpoints, and maintain structured audit logs across all tiers.
Organizations must define a comprehensive data retention policy, establish formal approval gates for high-impact infrastructure changes, and designate clear ownership for incident response. Developers must never expose database passwords, private keys, or internal service endpoints within source code repositories or client-facing telemetry output.
Identity and access
Security controls must never compromise system reliability or operational resilience. Engineering teams must rigorously test retry mechanisms, partial service failures, rate limiting, regional failover scenarios, and seamless rollback procedures. All side-effecting operations, such as database migrations or payment processing hooks, must be designed to be strictly idempotent.
Architects must continuously collect telemetry covering request latency, HTTP error rates, resource consumption, and dependency health. Comprehensive runbooks should clearly state how to safely isolate or temporarily bypass security features in the event of a false-positive blocking cascade, ensuring that business-critical workloads remain accessible during troubleshooting.
Runtime observability
Cloud security investments must be balanced against budgetary realities. Architects should carefully estimate the total cost of infrastructure, API transaction volume, storage retention, telemetry ingestion, networking bandwidth, and ongoing support. Benchmarking a representative workload against realistic traffic profiles yields far more accurate financial projections than relying solely on vendor pricing calculators.
Teams should configure Azure Budgets and cost alert notifications tied directly to specific cost centers and resource tags. When evaluating preview security capabilities or specialized WAF tiers, engineers must verify billing structures and service-level agreements (SLAs) prior to committing to production usage.
Final perspective
PHP Application Security on Azure should always be evaluated as a comprehensive architectural capability rather than a simple feature checkbox on a compliance audit. By starting with clear operational requirements, rigorously validating the current service contracts, and adopting security controls incrementally backed by empirical evidence from controlled pilots, organizations can run robust, high-performance PHP workloads with confidence in the Microsoft Azure cloud.
Further reading
Microsoft documentation for configuring PHP on Azure App Service. Verify the latest runtime versions, configuration directives, and related release notes before scheduling production deployments.
More articles on Cloud Security are available in the blog archive.